Show whether remediation activity is producing the expected change in risk.
Remediation reporting often records activity completed without showing the resulting change in exposure. CRI provides a consistent quantitative view over time, helping leaders assess whether agreed actions are producing the expected risk reduction and where further intervention may be needed.
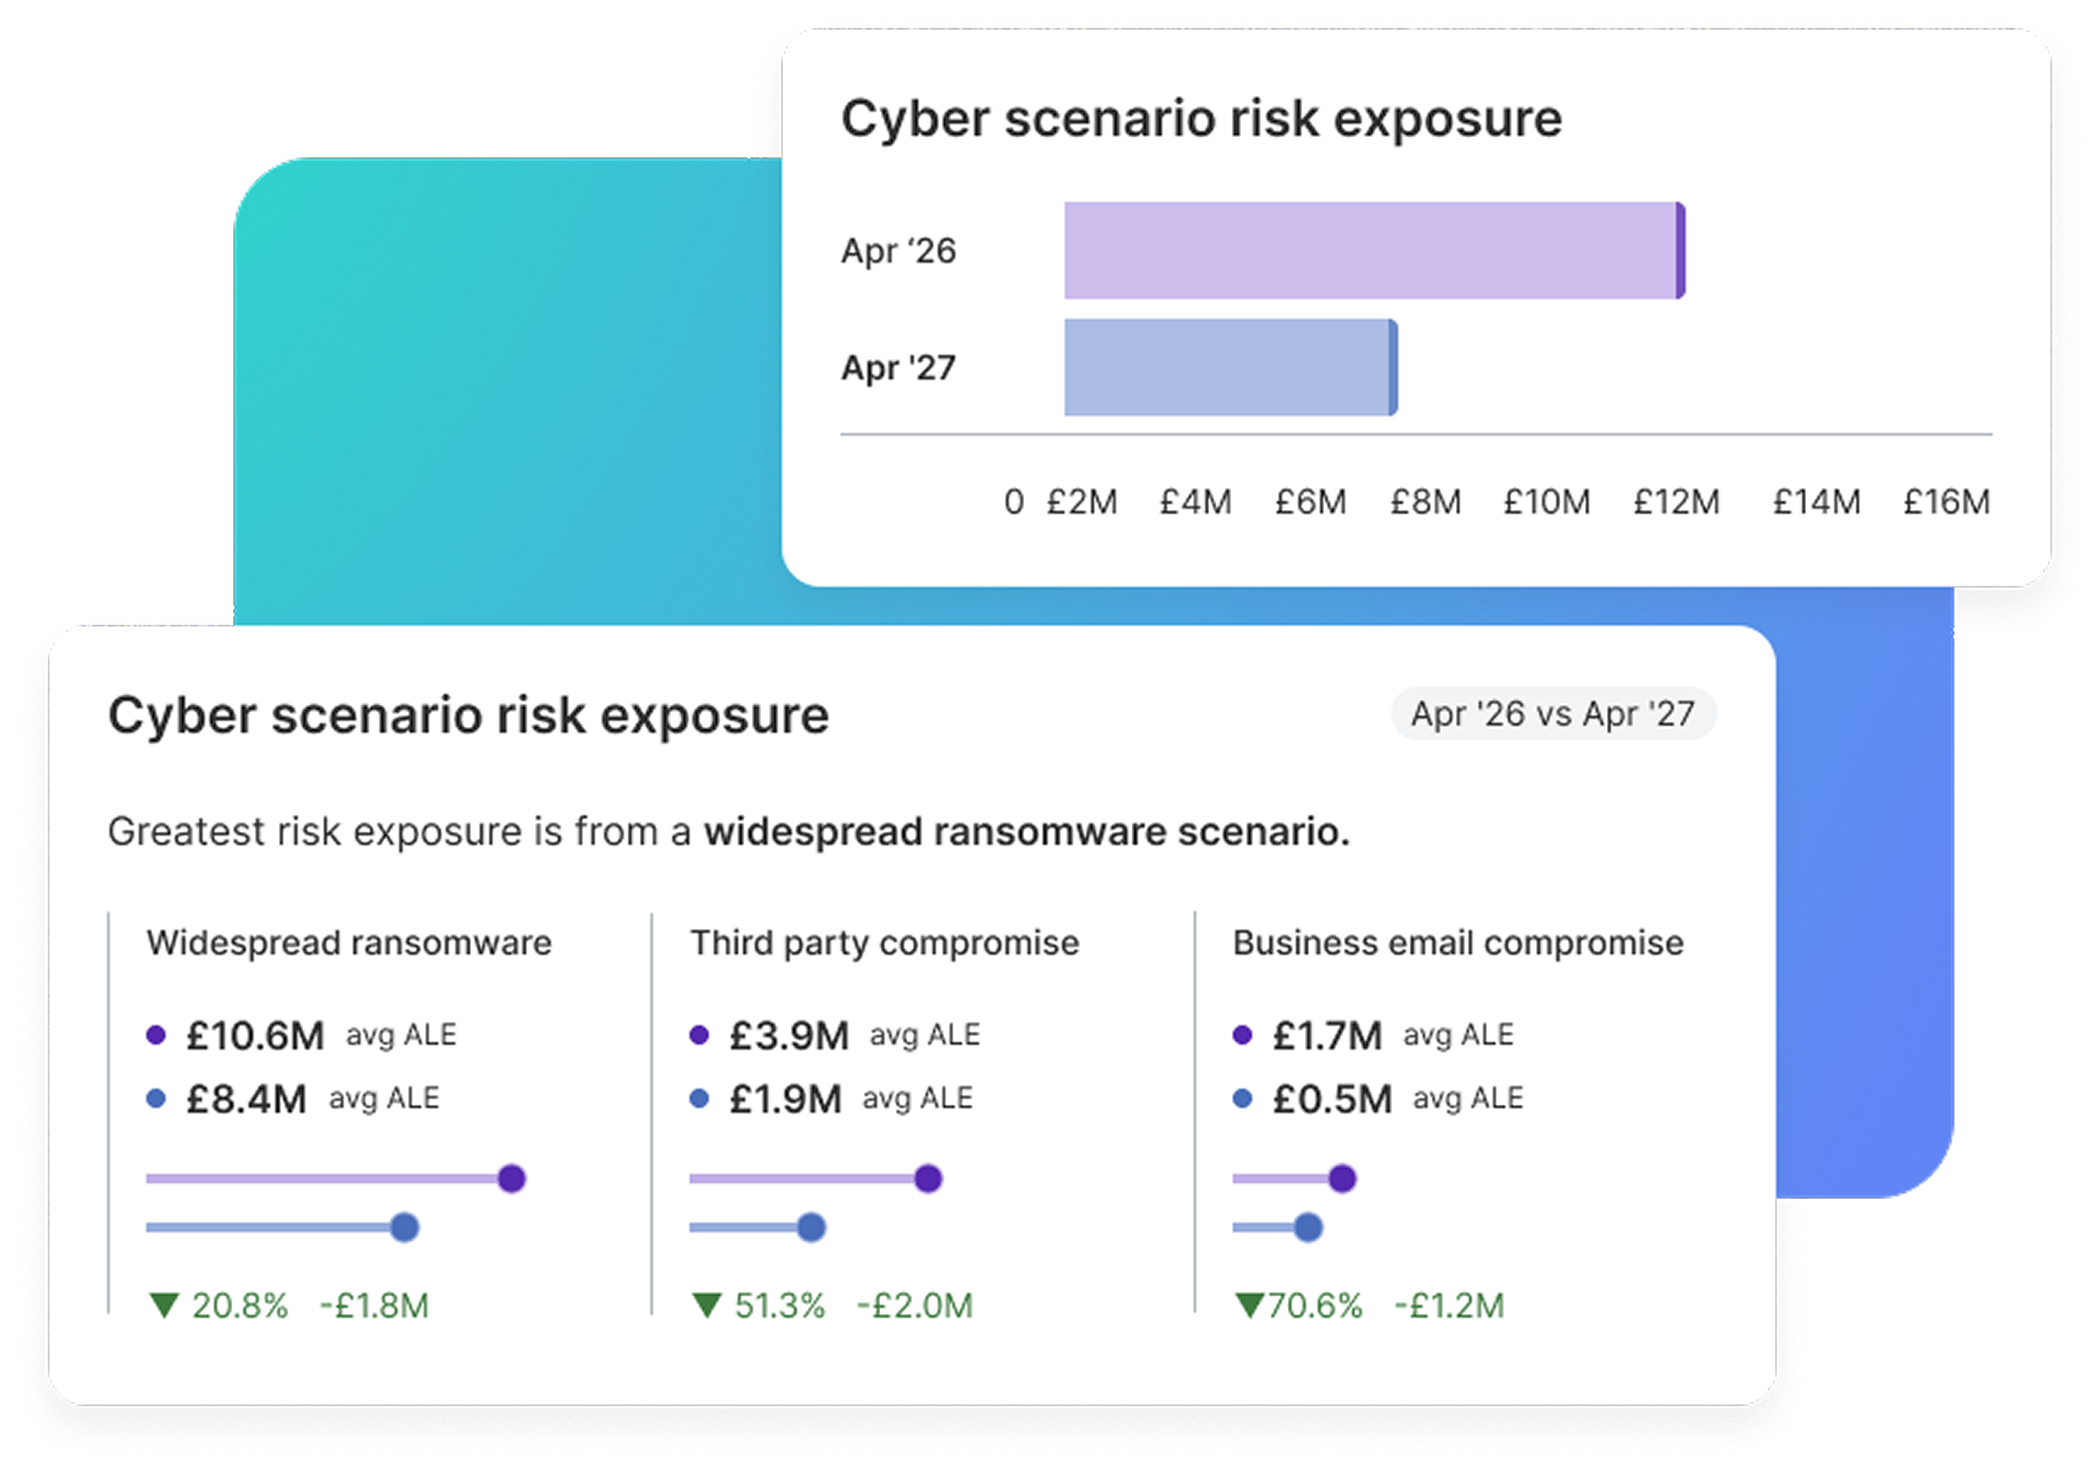
Compare overall and scenario-level exposure across assessment periods.
Track progress against risk appetite and agreed risk-reduction objectives.
See where exposure is reducing, stable or increasing.
Are remediation plans delivering the expected result?
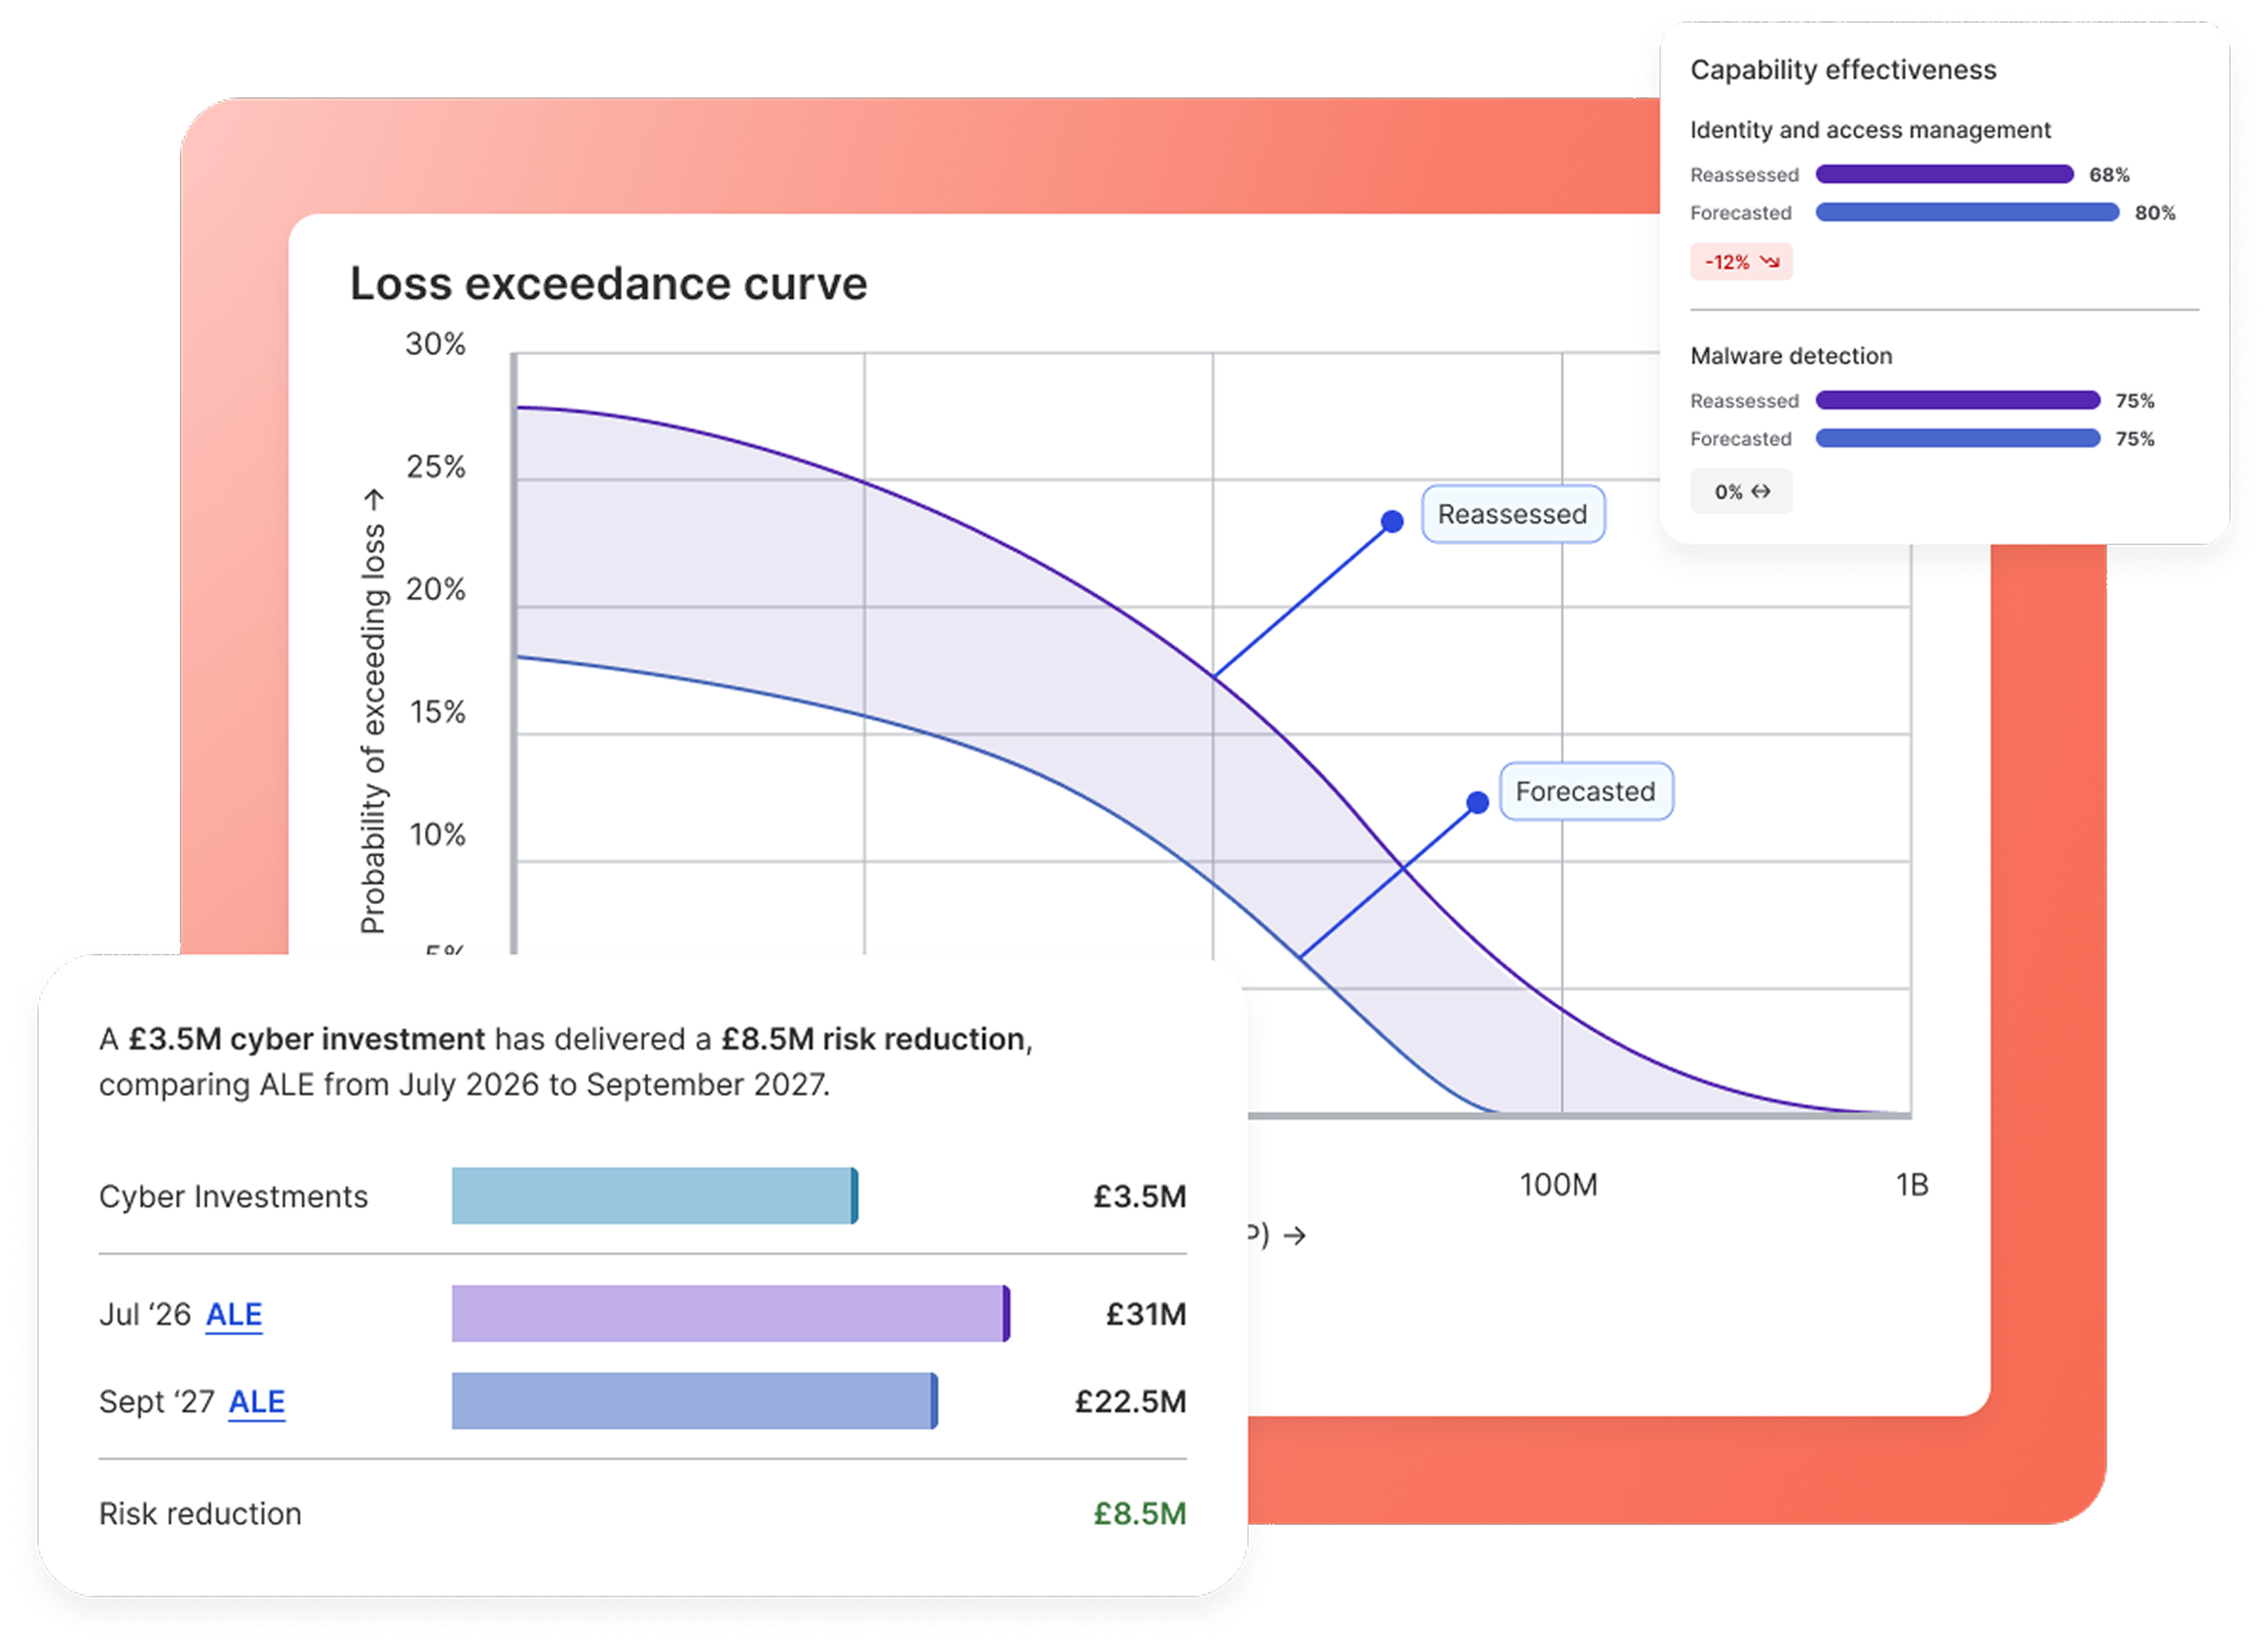
Compare the risk reduction expected from agreed actions with reassessed exposure.
Identify where delivered improvements have changed the risk position.
Highlight gaps between the expected and observed result for further review.
What clients say
Working with CRI over the past few years has helped us steadily strengthen our cyber posture. Through structured assessments aligned to relevant compliance frameworks, we’ve been able to demonstrate to leadership that our cyber investments are well placed and are reducing our loss exposure. The CRI team and platform have provided valuable insight to support more informed prioritisation of cyber initiatives and better allocation of resources.
Boryana Kulinska, Head of governance, risk and compliance myPOS