Prioritise third-party riskusing a comparable financial view of exposure.
Third-party assessments can generate large volumes of technical findings without showing the financial exposure individual dependencies create for the organisation. CRI quantifies that exposure, helping leaders compare dependencies,identify concentrations of riskand direct action towards the relationships that matter most.
Which third-parties create the greatest exposure for our organisaiton?
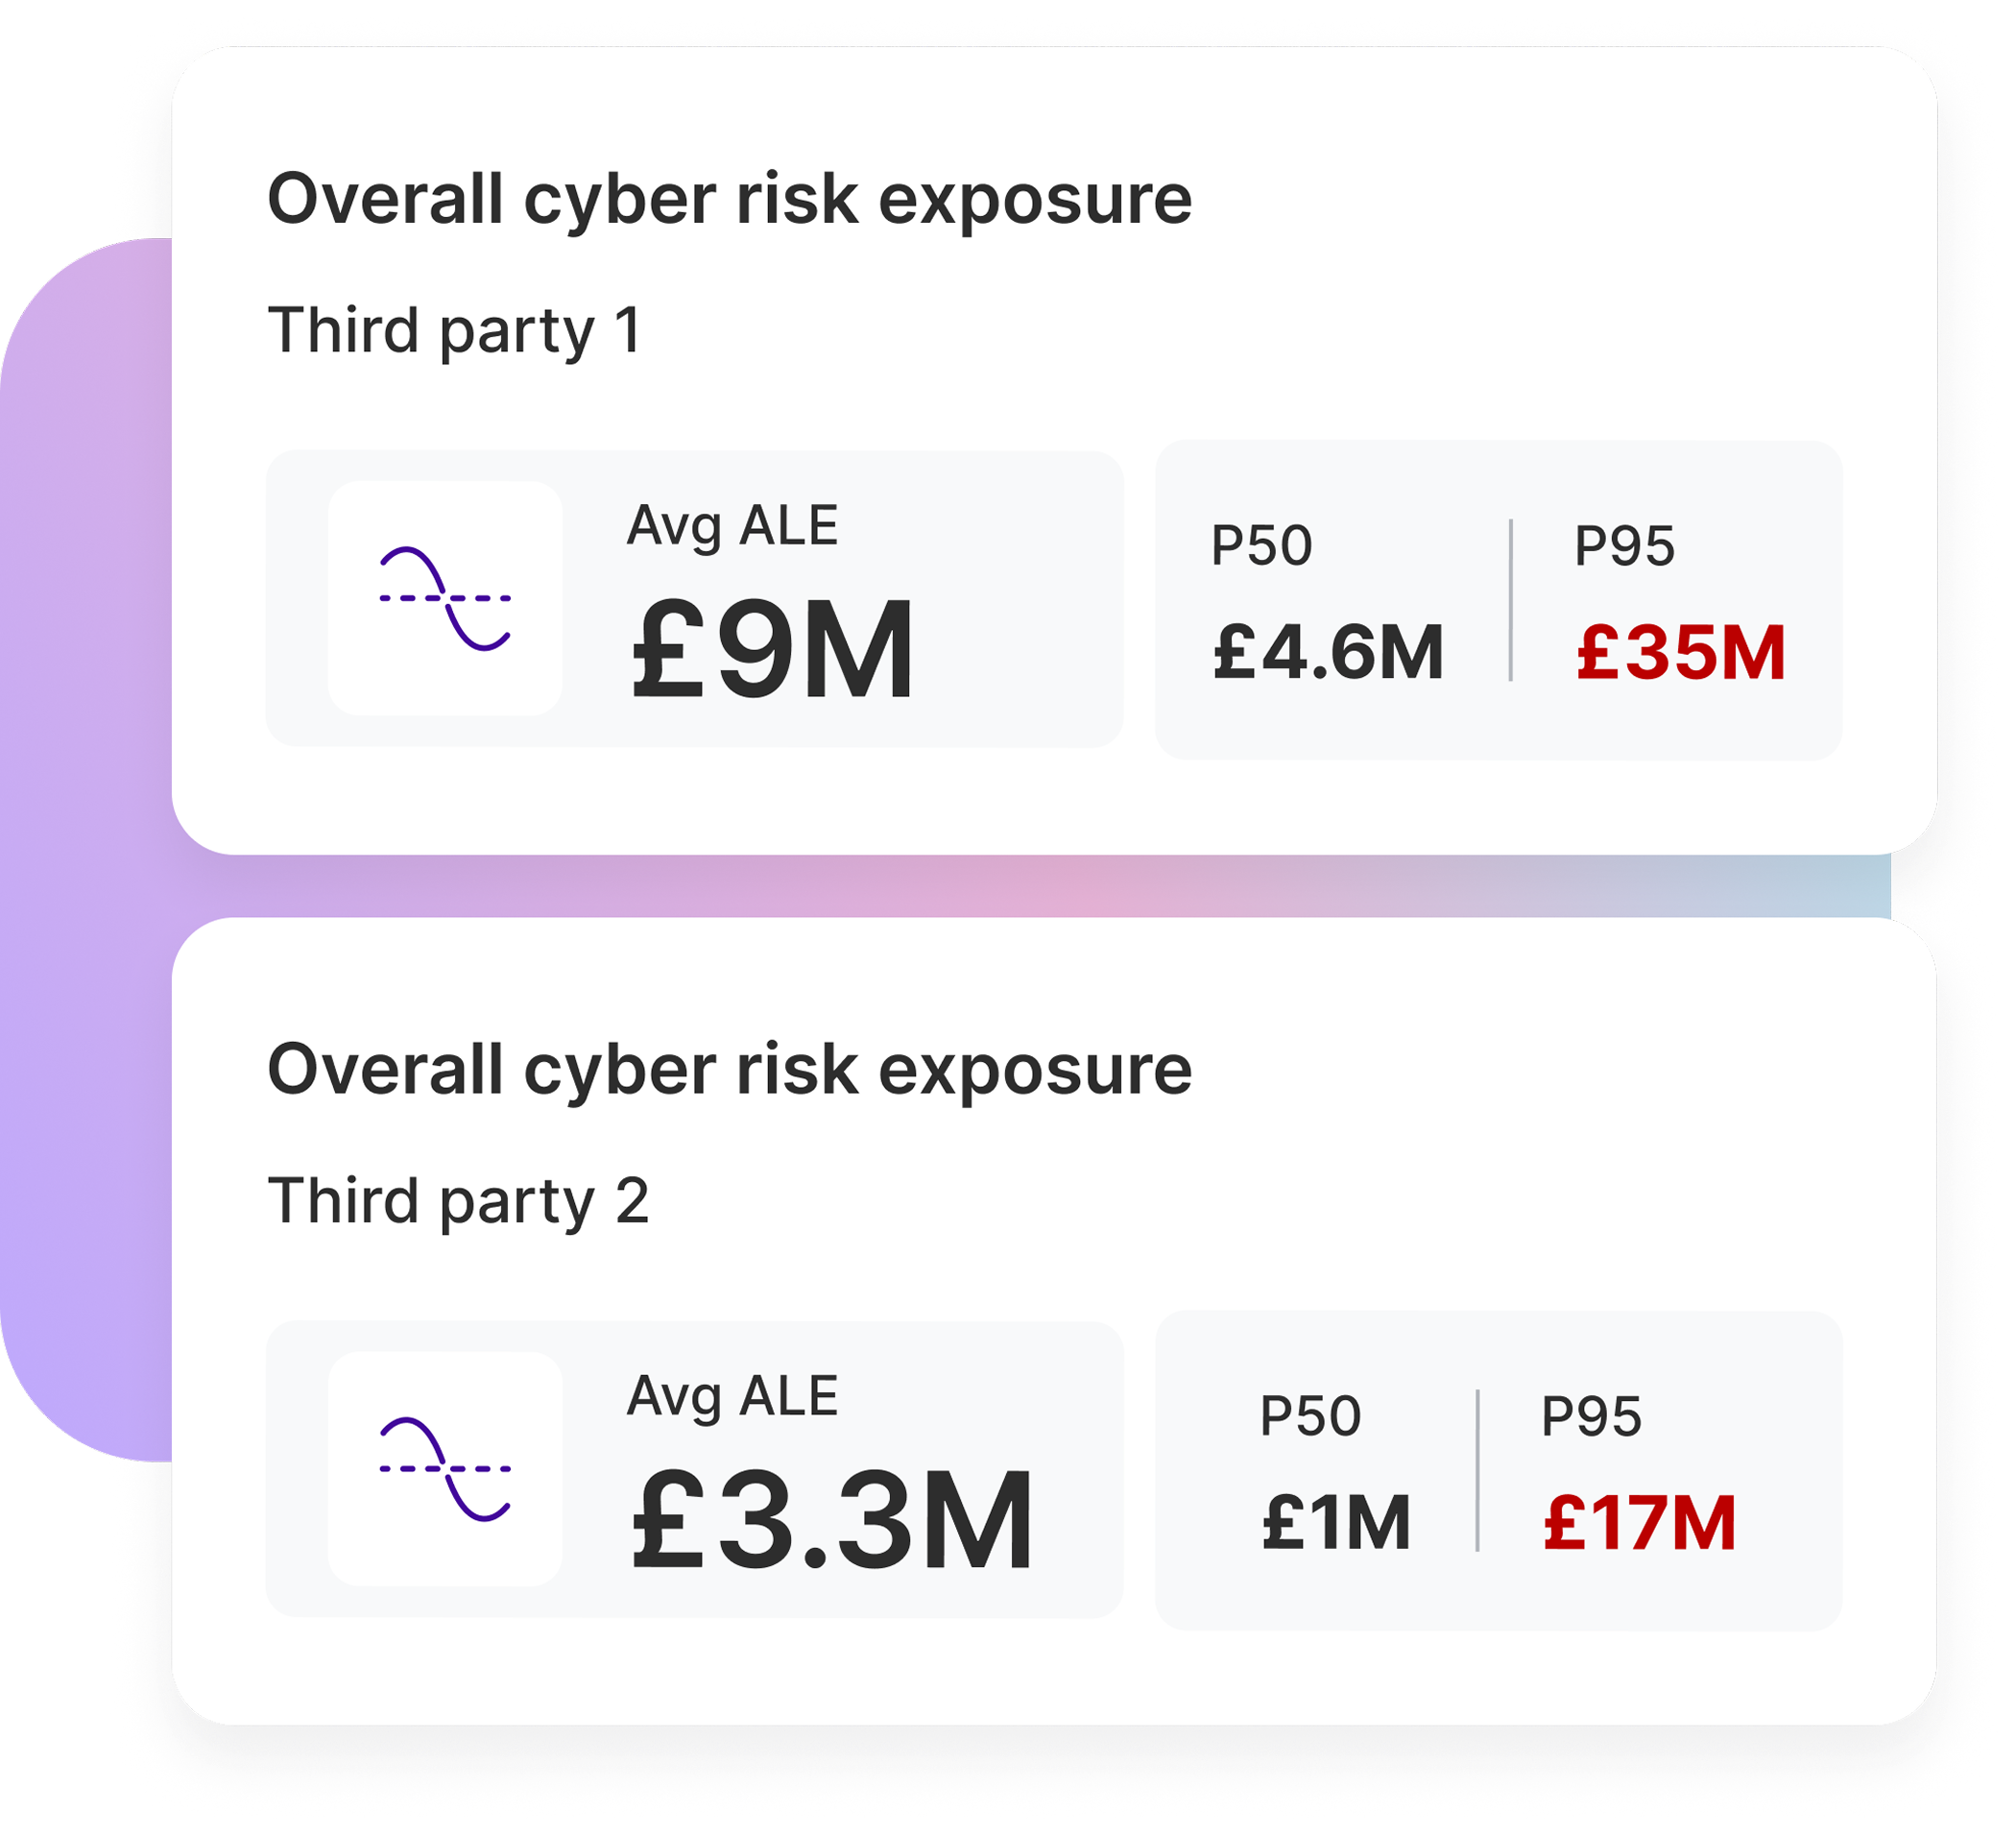
Estimate the average annualised loss exposure associated with each dependency.
Compare the potential range and severity of loss across third parties.
Identify concentrations of exposure and prioritise deeper review or treatment.
What is driving a third-party's financial exposure?
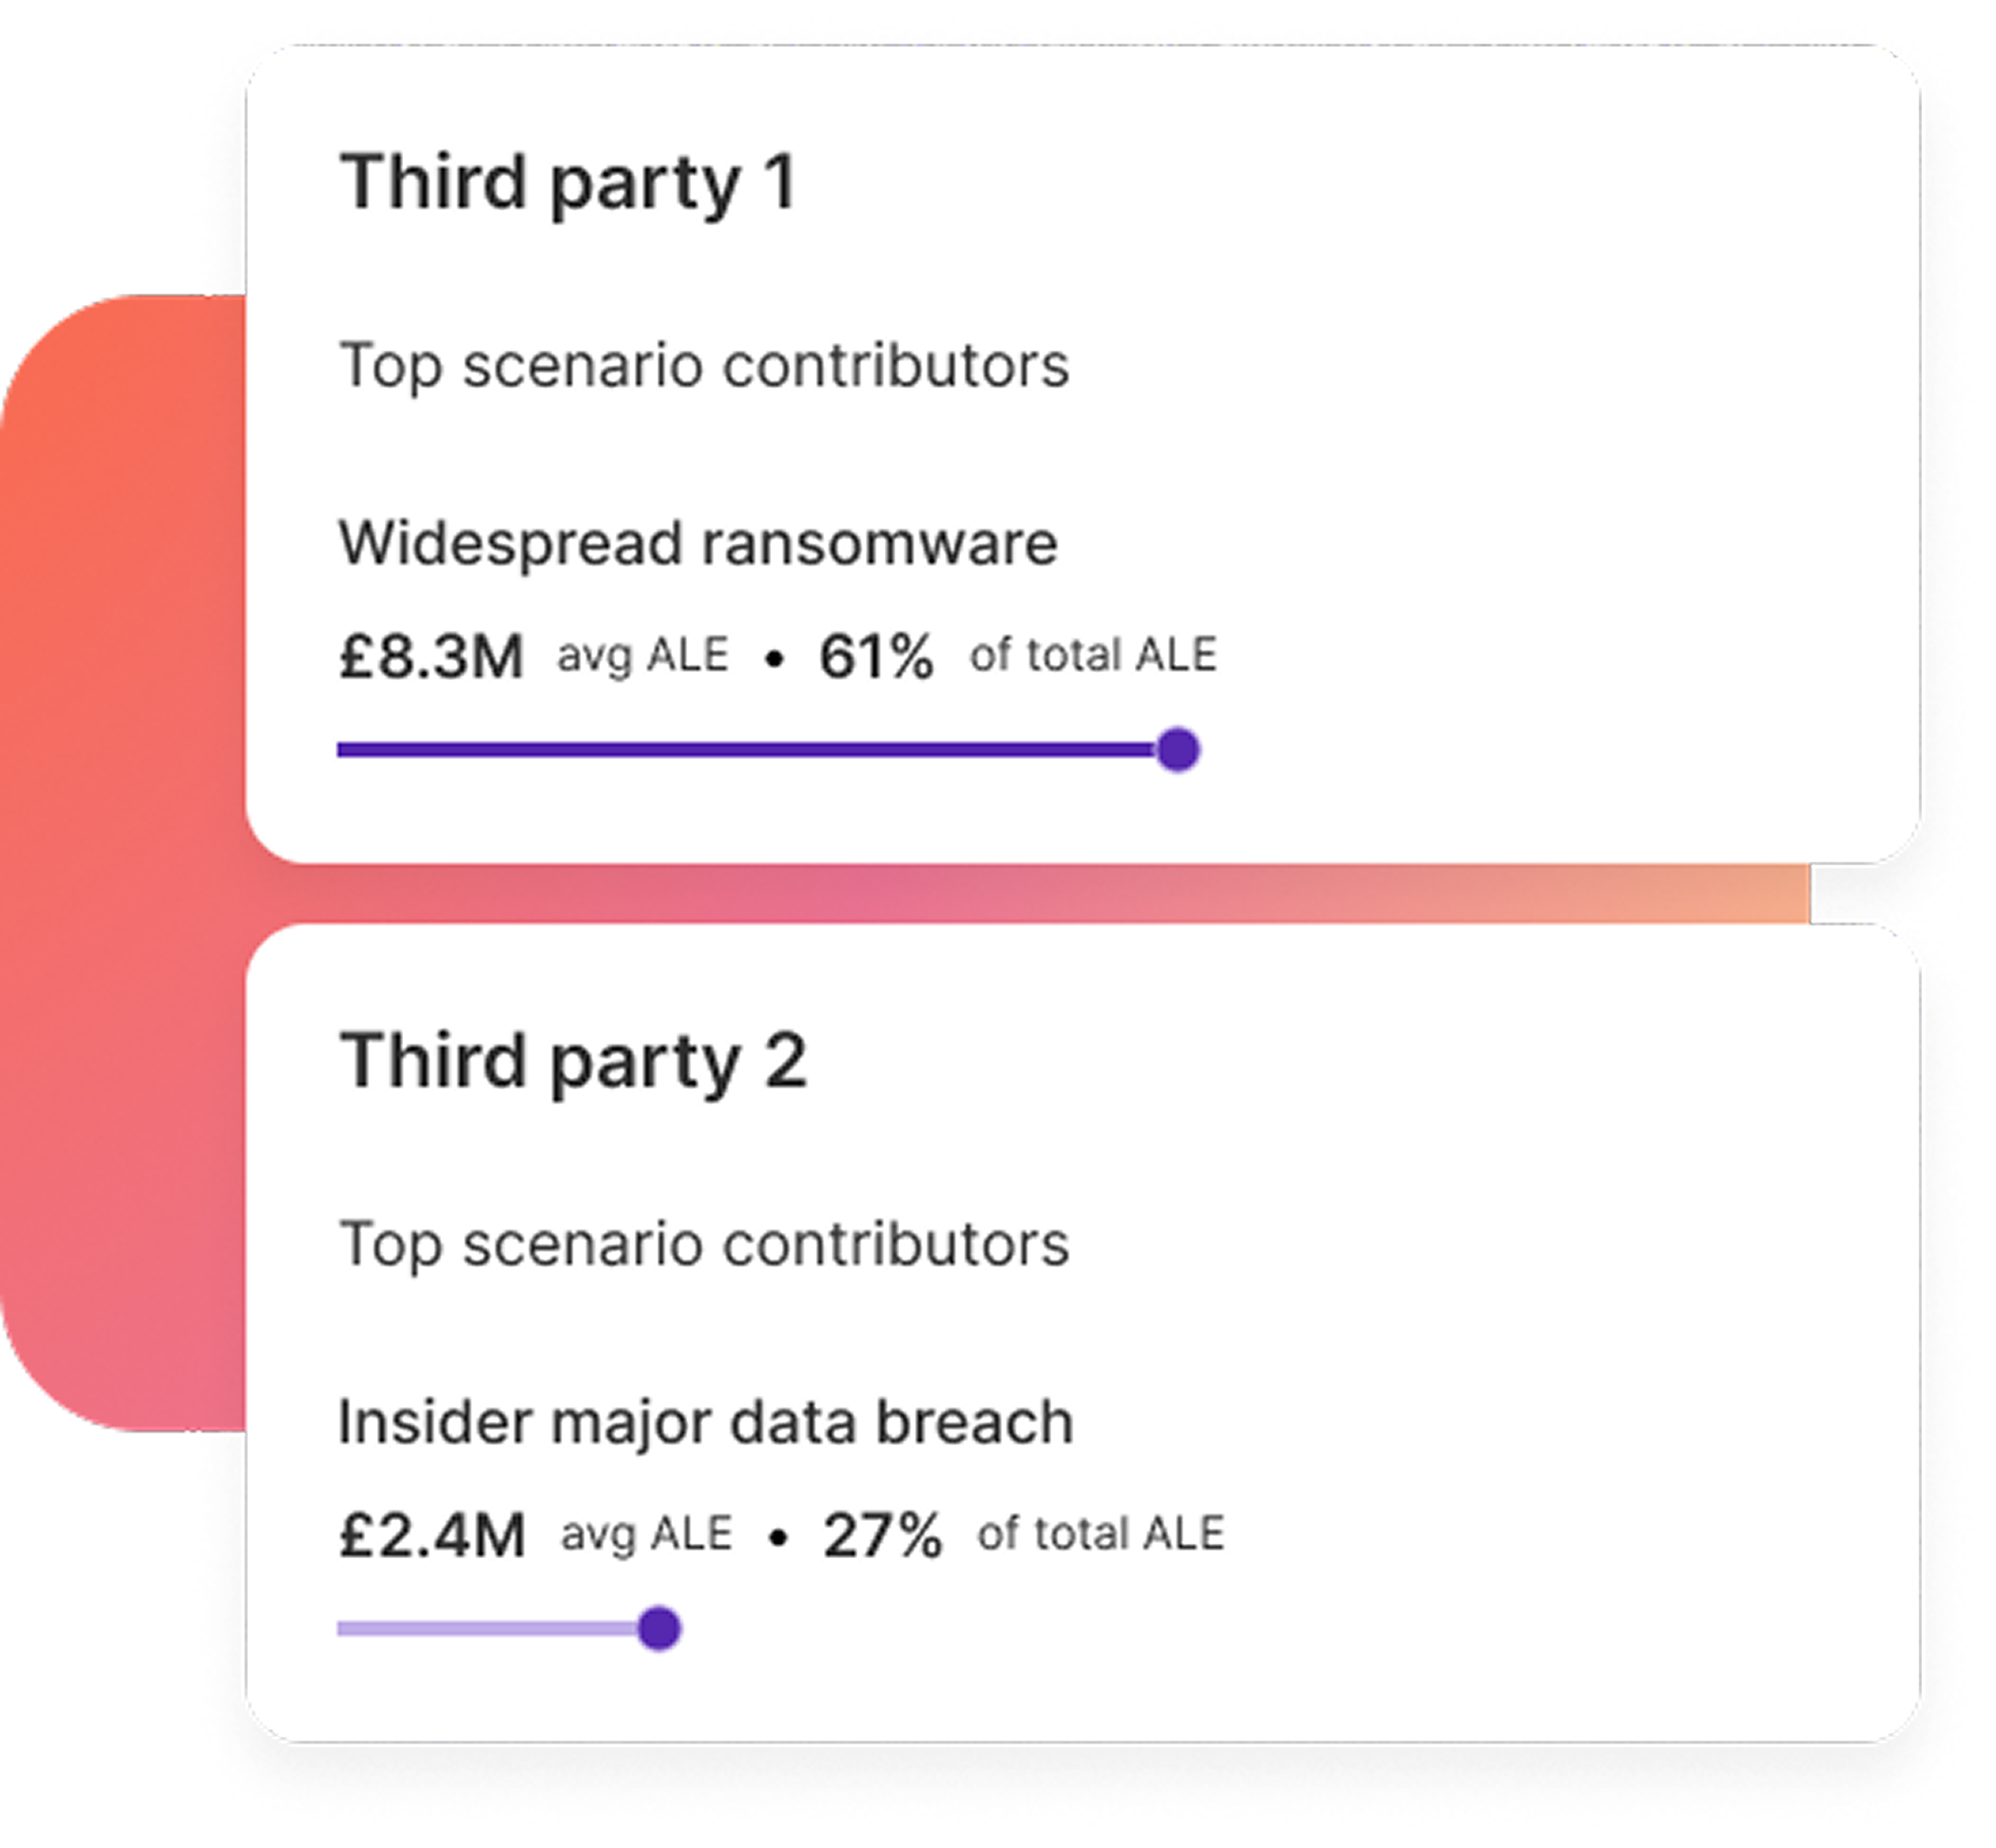
Identify the threat scenarios contributing most to exposure associated with the third party.
See which business units, services or processes depend on that relationship.
Explore the principal loss events and assumptions shaping the financial result.
What clients say
CRI has been a strategic enabler for our business. The value it has delivered already is significant, and we have used the data to inform and guide us in different governance forums. We have tested other solutions and none has delivered the value CRI has.”
Group cyber and resilience lead Global packaging manufacturer
The UK Cyber Security and Resilience Bill is moving supply chain security from compliance to calculus. The days of managing third-party risks with just questionnaires are over. It's time for a new approach.